Lighter’s exploit raises uncomfortable questions for Hyperliquid’s $5.7 billion market
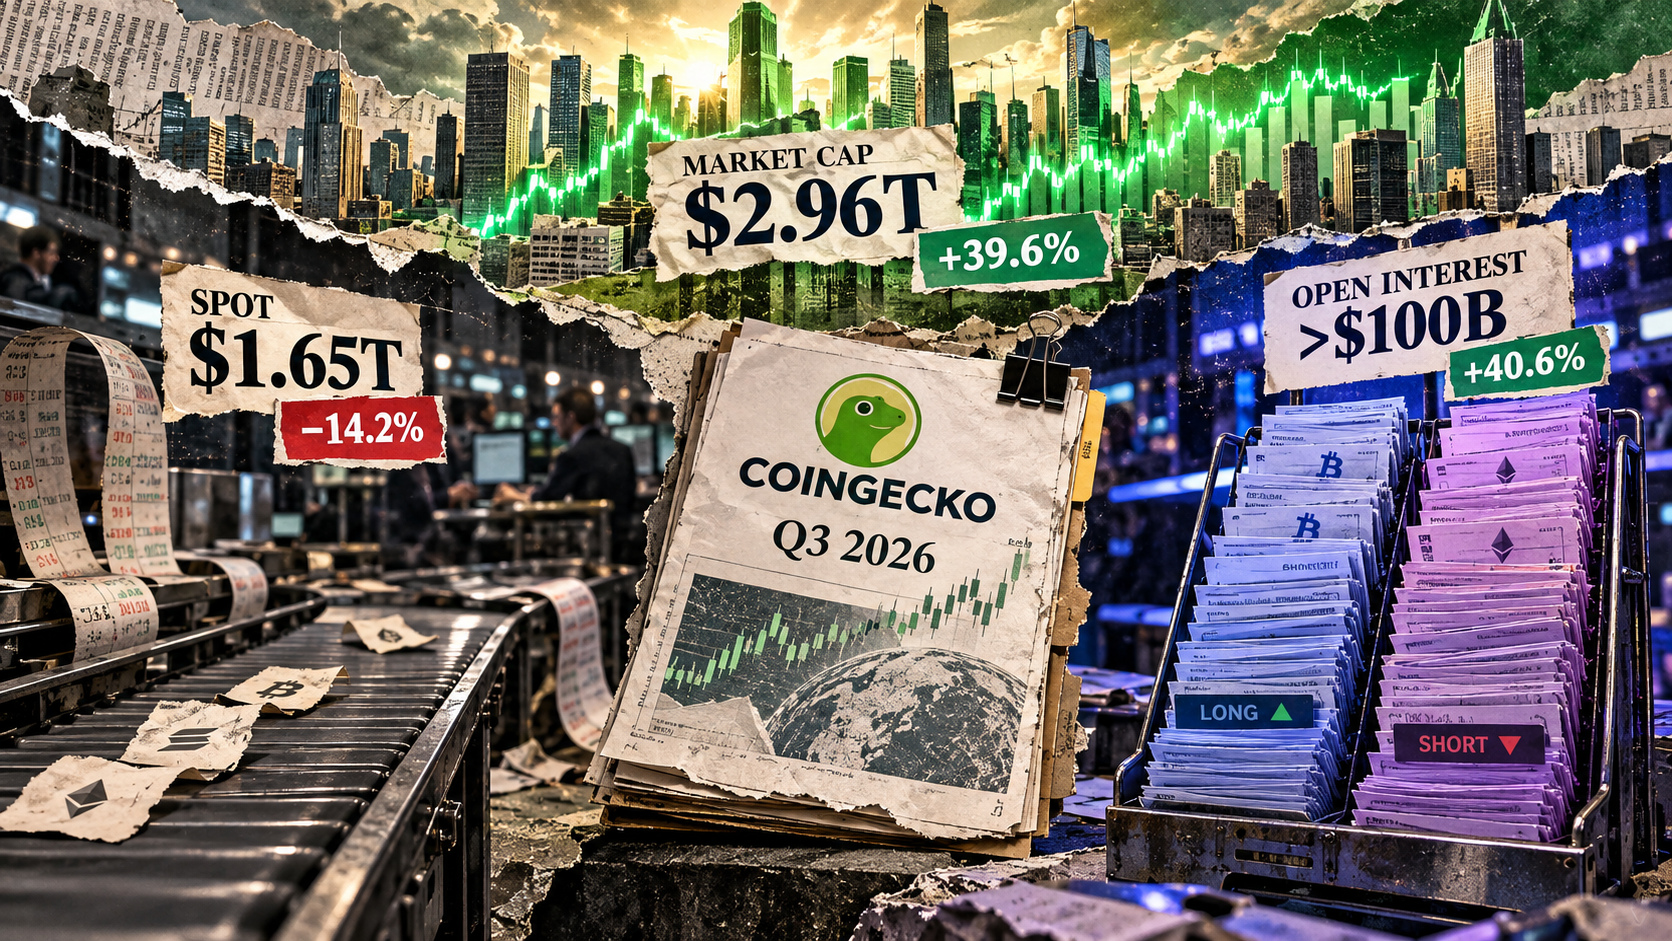
Lighter said exposed API keys, recovered through reused signing nonces in unsafe third-party code, enabled an attacker to drain funds through a public-pool share-accounting flaw. It reported that withdrawals resumed and about 5 million USDC was returned, while adding wallet-signature requirements, IP allowlists and configurable limits. A separate blockchain analysis traced a 10.39 million USDC withdrawal but could not verify all reported losses. The incident does not establish that Hyperliquid has the same vulnerability. Its agent permissions and transfer paths vary; a compromised agent could cause losses through unauthorized trading and liquidation, while broader effects would depend on positions, liquidity and market depth. Hyperliquid had about 5.7 billion dollars in open interest, roughly 55% of the tracked total, but that scale alone does not show how much a specific compromise could affect.