Hackers found a way to steal Bitcoin without private keys
Summary
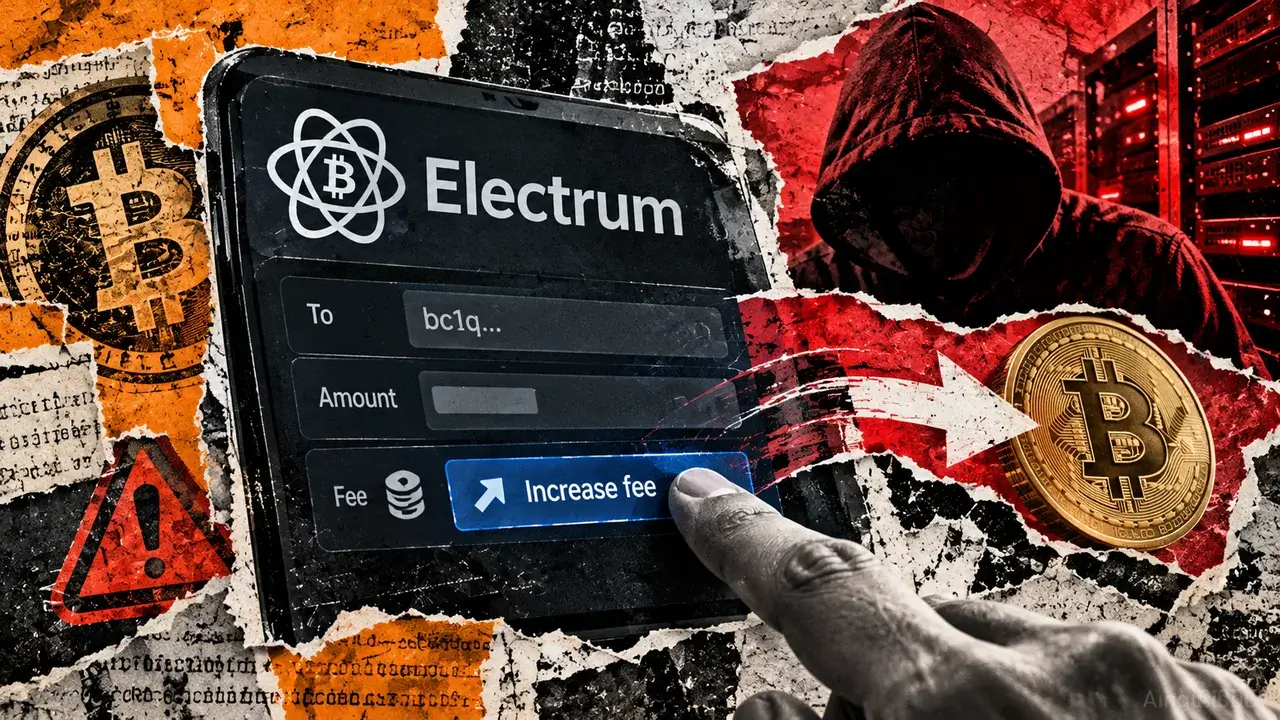
Electrum patched a high-severity flaw in versions before 4.8.3 that let malicious servers substitute attacker-controlled Bitcoin transactions in users’ unconfirmed transaction history. Users who tried to raise fees could sign the altered payments, sending funds to attackers without exposing private keys. Developers confirmed active exploitation and at least one reported loss, though they did not disclose the amount stolen. The update adds signature checks for wallet-owned inputs. Users should upgrade, verify full recipient addresses and amounts, and use trusted servers; the advisory says clients connected only to trusted servers were not vulnerable.