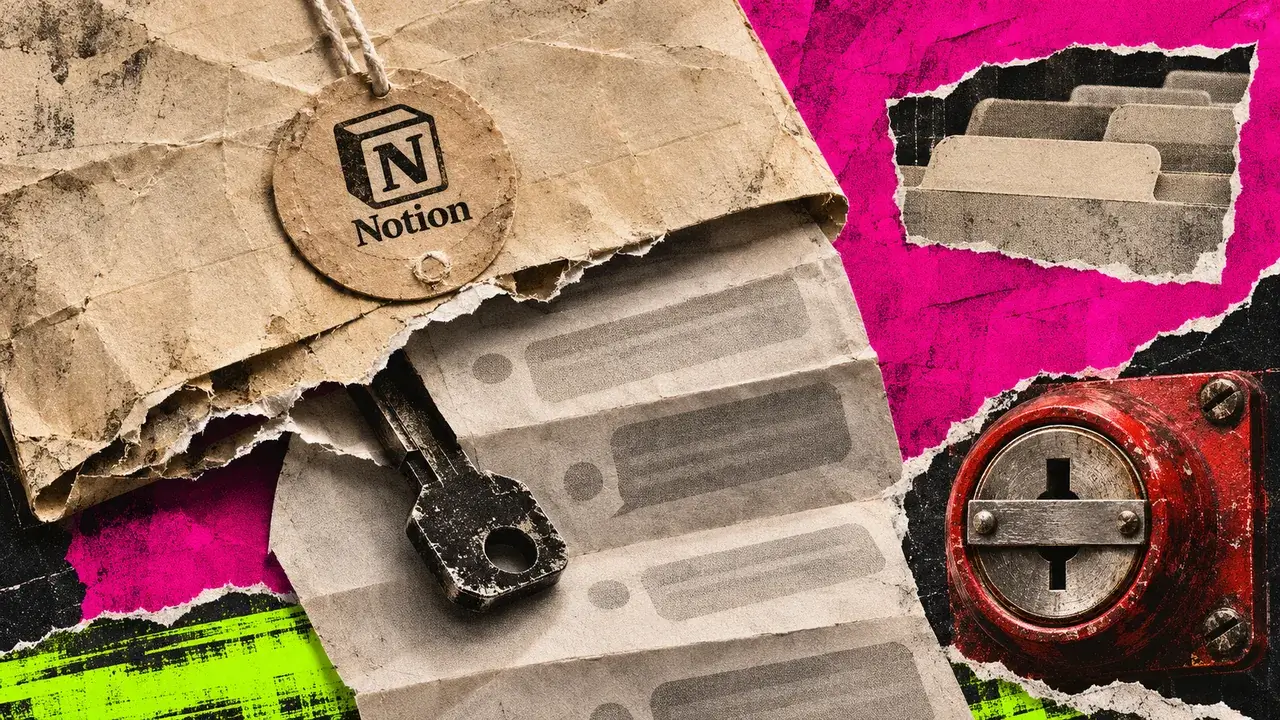
Notion users put access keys in AI chats. A supplier breach exposed them
Summary
Notion revoked API keys found in AI chat transcripts exposed through a breach at supplier Fireworks AI. Fewer than 1% of Notion workspaces were affected; transcripts could contain information linking chats to users or companies, and keys could access workspace data within their permissions. Notion says it found no evidence the revoked keys were misused, disabled its Insights feature and stopped serving open-weight models through Fireworks. It advises affected customers to treat relevant chat content as exposed and rotate credentials pasted into Notion AI during the incident period. The investigation is ongoing.