Cursor urges credential resets after malicious Claude Code marketplace update
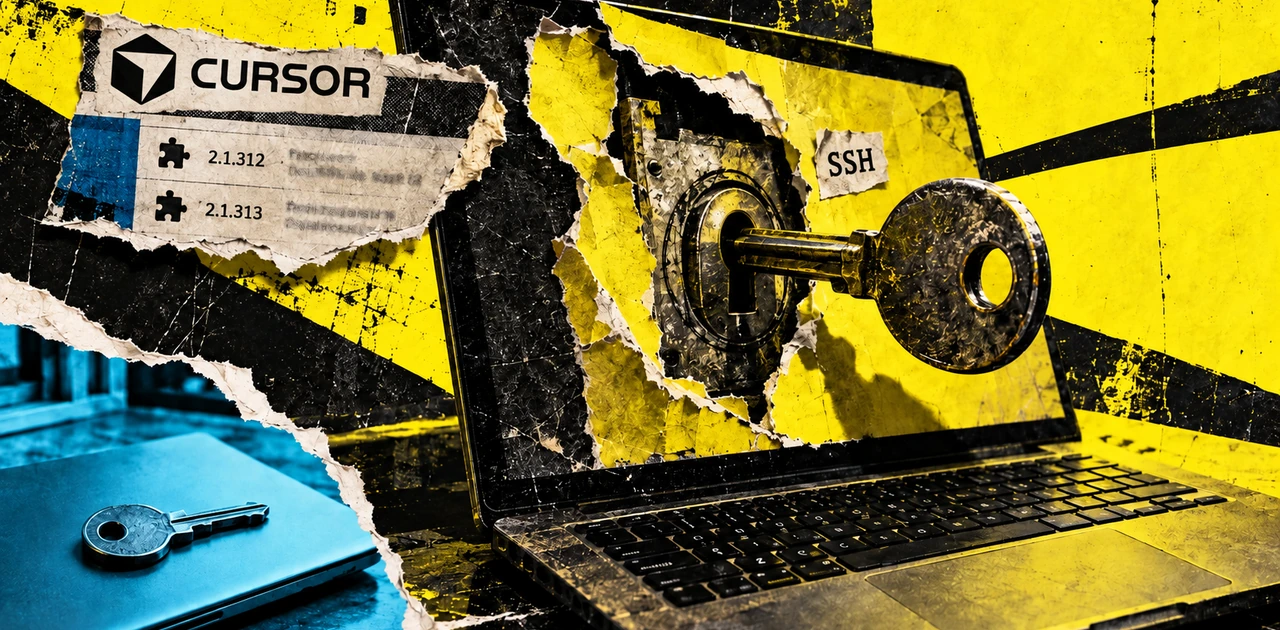
Cursor warned users of malicious Claude Code extensions versions 2.1.312 and 2.1.313, available for macOS and Windows on Oct. 29, to clean affected machines and rotate credentials and sessions from a trusted system. The payload could install an attacker SSH key, enable remote login, create a reverse tunnel and persist through startup mechanisms. Removing the extension may not remove these components. Remote access depended on host conditions, and researchers found a macOS permission bug that could prevent SSH activation for standard users. Cursor took the packages and attacker server offline and rebuilt its marketplace, but says these steps do not clean infected machines. No cryptocurrency theft or crypto-specific targeting has been established; crypto developers should assess credentials accessible from affected hosts.