The catch in recovering a hacked crypto wallet: the thief may still have a key
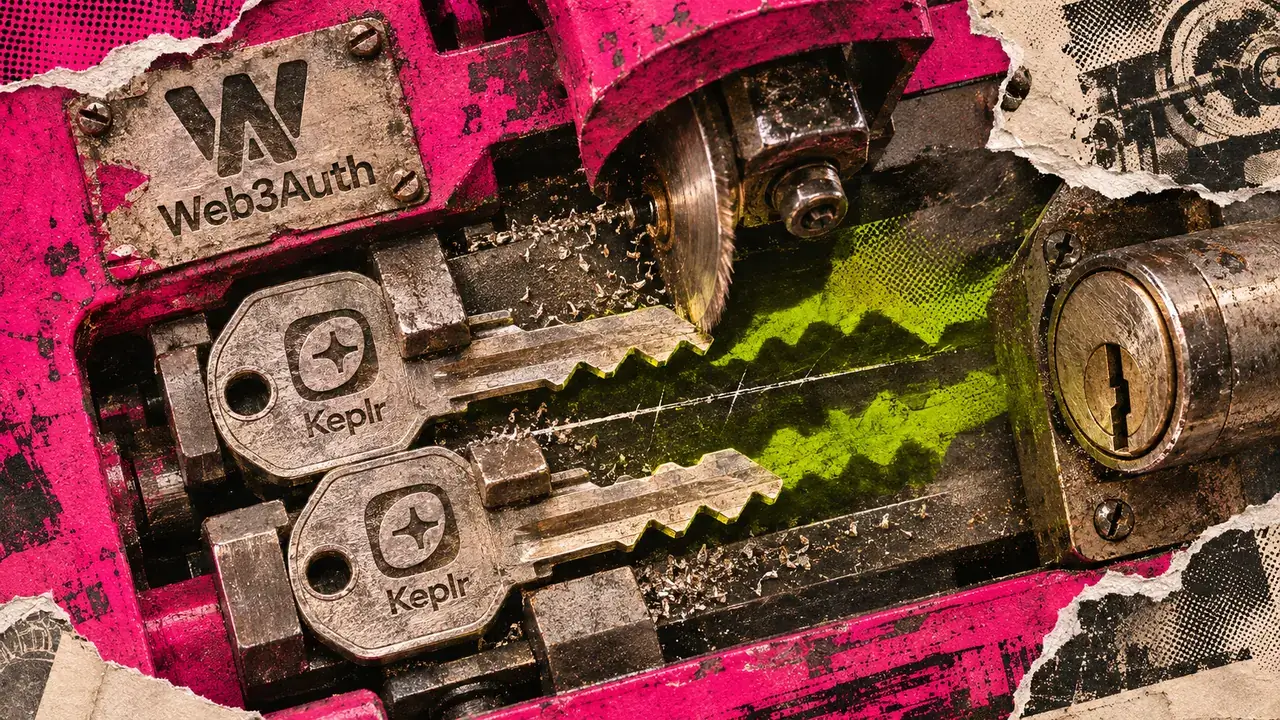
Keplr paused Google and Apple logins on Nov. 7 after unauthorized transactions were reported. Web3Auth said a security issue in its infrastructure affected some embedded Keplr wallets; Keplr later warned that private keys for some social-login accounts may have been compromised. Users were advised not to add funds and to move remaining liquid assets to recovery-phrase or hardware-wallet accounts. Keplr’s documentation describes exporting and importing private keys independently of Google sign-in, but that route is not confirmed as usable during the pause and cannot make a potentially exposed key safe. Web3Auth and partners began whitehat recovery efforts for vulnerable wallets, while some balance changes may reflect mitigation activity. Recovery-phrase and hardware-wallet accounts were reported unaffected. Restoring login access alone would not resolve account security or asset-recovery questions.