A 20-month Polkadot wallet breach reveals the dark side of faster crypto withdrawals
Summary
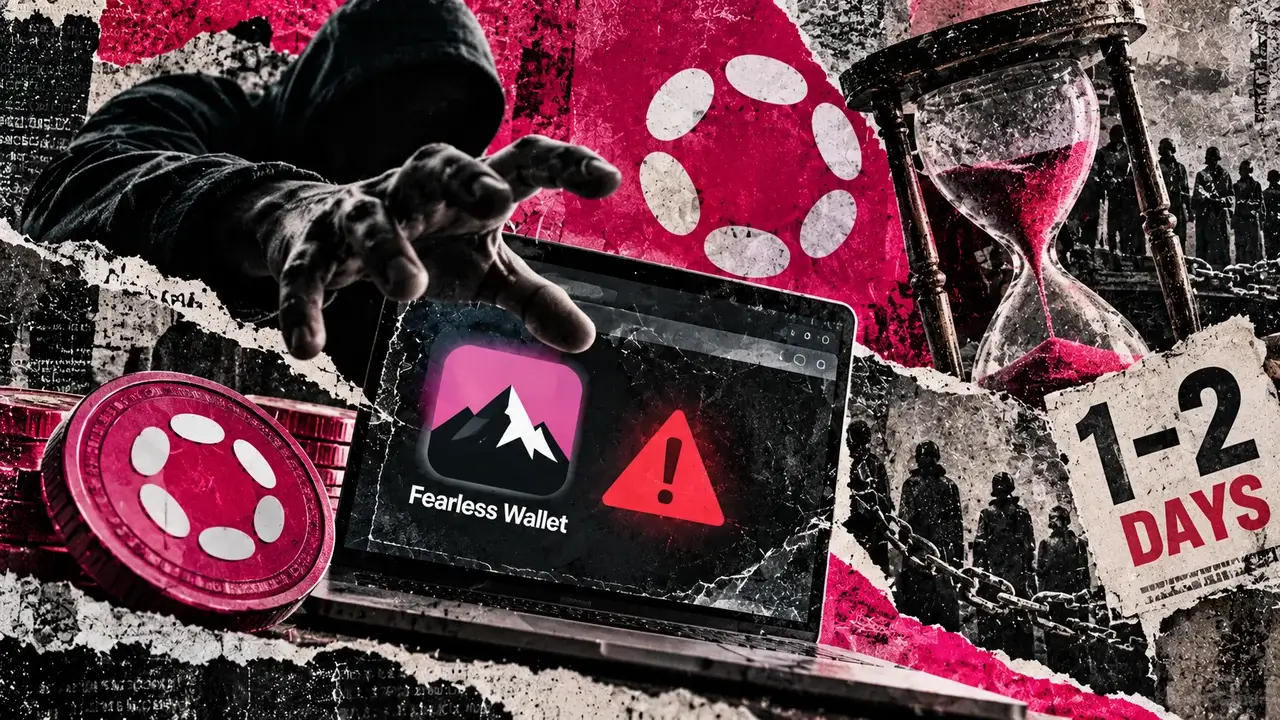
A malicious Fearless Wallet browser extension exposed users’ private keys and recovery phrases from February 2025. Polkadot reported eight users with unauthorized transfers totaling 17,286 DOT; affected extension versions were 3.0.1 and 3.0.3–3.0.5. Users are urged to create entirely new credentials and move remaining funds. The incident has renewed concern about Polkadot’s July change that cut nominator unbonding from up to 28 days to about one or two days, leaving less time to intervene if a compromised account begins unstaking. However, investigators have not linked the shorter period to the reported thefts. Locked funds may have recovery options while protocol restrictions remain, but recovery is not guaranteed.