A Midnight privacy-vault demo needs outside signers to release Ethereum tokens
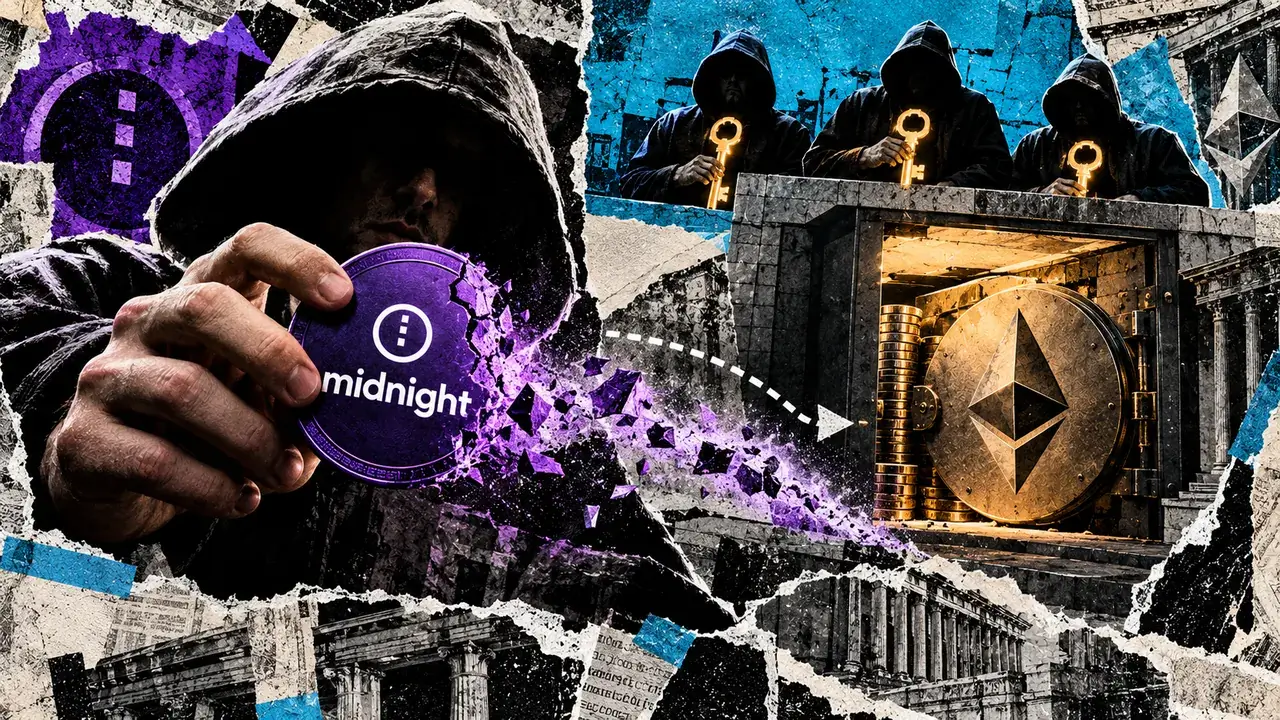
SIG’s experimental Ethereum vault holds ERC20 assets on Ethereum while users hold shielded claims on Midnight. Withdrawals burn a claim, then rely on SIG’s threshold-signing service and a separate attestation of the transaction outcome; verified failures can restore the claim, but missing responses alone cannot. Emergency nonce replacement also depends on signing and attestation and may race an unsigned request. The integration remains at stagenet/testnet stage, with no published mainnet vault address. A demo using a fake MPC responder does not prove production signers are operating, and the cited audit covers Solidity chain-signature contracts, not the newer vault or full Nightmode system. Production readiness therefore depends on evidence about deployed code, signer and attestation arrangements, audit scope, and recovery procedures.