Crypto hackers exploit third-party Aave tool to steal 114 ETH
Summary
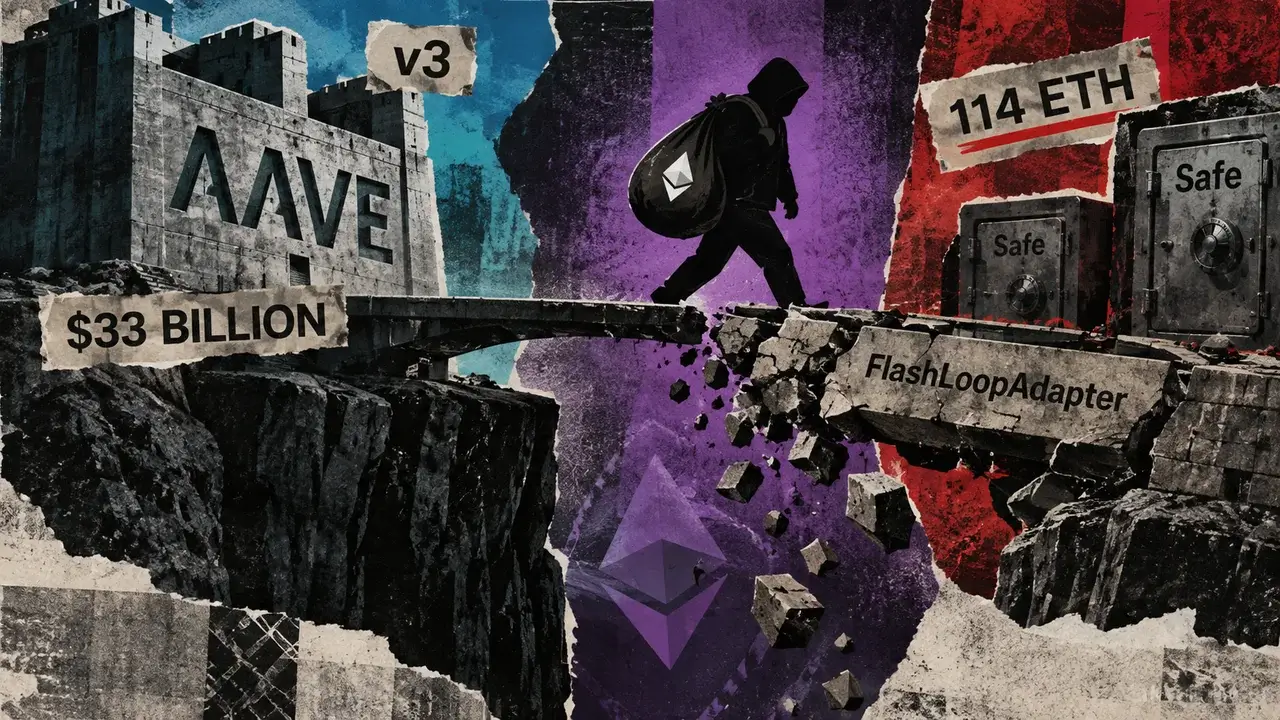
An attacker exploited a flaw in the FlashLoopAdapter, a third-party adapter used with Aave v3, and stole about 114.09 ETH (over $300,000) from two Safe multisig wallets. SlowMist said the adapter’s module-authentication check could be spoofed with a fake Safe, while caller-controlled router and calldata enabled transactions through the victims’ wallets and withdrawals of collateral. About 1,300 WETH of debt was also repaid to unlock collateral. Aave founder Stani Kulechov said Aave v3’s core contracts were not affected; the exposure was limited to users of the adapter.