Eclair patches a browser attack that could send commands to your Lightning node
Summary
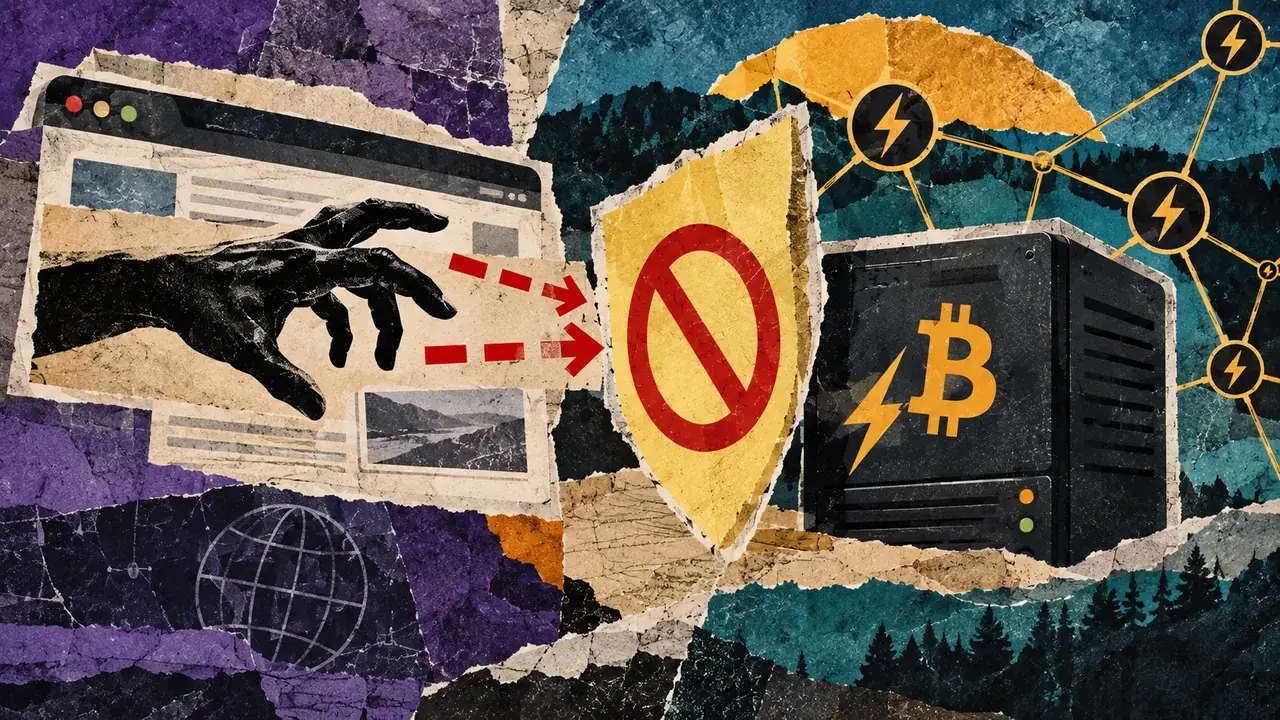
Eclair, ACINQ’s Bitcoin Lightning node software, released v0.14.4 with a fix for malicious webpages that could use a browser’s cached HTTP Basic credentials to send commands to an exposed node API. The API can manage channels and payments. The patch rejects requests containing an Origin header before they reach API routes, which also means browser-based interfaces need a backend intermediary. Command-line tools remain unaffected. Maintainers stress that operators must still keep the API bound to loopback and retain appropriate authentication and network restrictions. They recommend upgrading; the node can be restarted without closing Lightning channels.