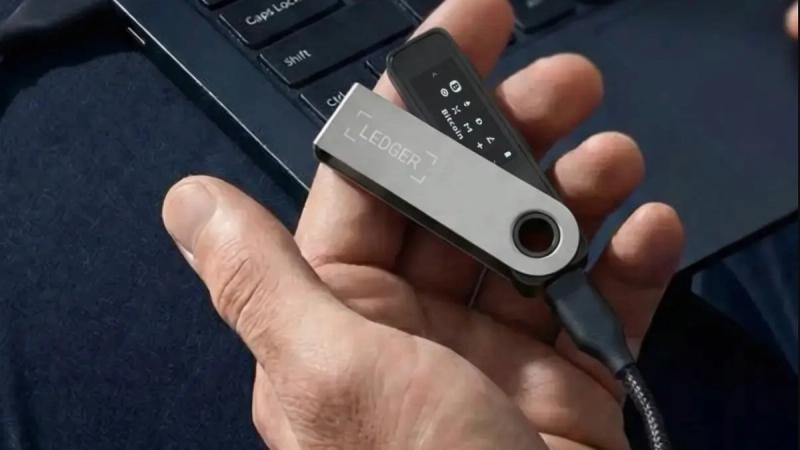
Ledger finds covert cellular implant stole hardware wallet recovery phrases from screens
Ledger said a hardware implant in some devices sold by Southeast Asian reseller CryptoBilis captured users’ 24-word recovery phrases during setup and sent them via LTE using an eSIM. The physical supply-chain attack did not compromise Ledger’s secure element, software, or transaction signing. Ledger confirmed one implanted device and said all confirmed losses in the Oct. 9 incident involved CryptoBilis-sold devices; it has not verified reports involving other sources. Ledger has not confirmed victim numbers or losses, while researchers estimate up to $93.2 million stolen across more than 300 wallets. Tether froze $10 million in related USDT. CryptoBilis has stopped selling Ledger devices. Ledger advises buyers not to initialize affected devices and previous users to transfer assets to a new device with a fresh recovery phrase.