Ledger Says Coldcard Exploit Shows Bitcoin Wallet Security Must Adapt to AI
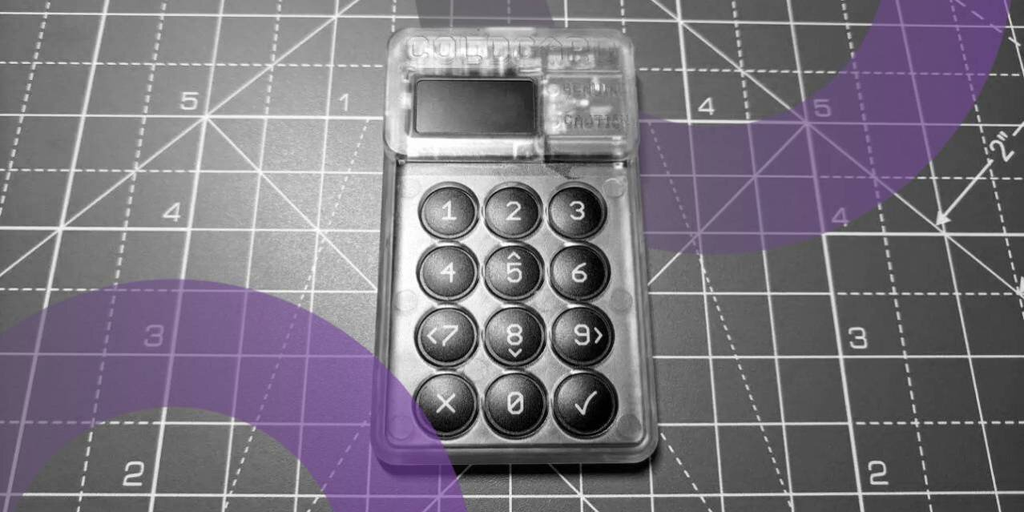
Ledger says the Coldcard exploit is a warning that hardware wallet security depends on strong randomness. A flaw in Coldcard firmware used a software fallback instead of the hardware random number generator to create recovery seeds, making some private keys guessable and enabling thefts now estimated at about $130 million. Coinkite has patched the issue and told affected users to move funds. Ledger says its wallets were not affected because they generate 24-word recovery phrases from a true hardware random number generator inside a certified Secure Element, with no software fallback. The incident also highlights how AI is accelerating both attacks and defense: attackers can scan code and spot flaws faster, but defenders must use AI, human review, and secure-by-design engineering just as quickly. Ledger advises users to check how a wallet generates entropy and whether that process is independently certified.