Microsoft exposes how USDT-funded phishing network targeted 75,000 organizations
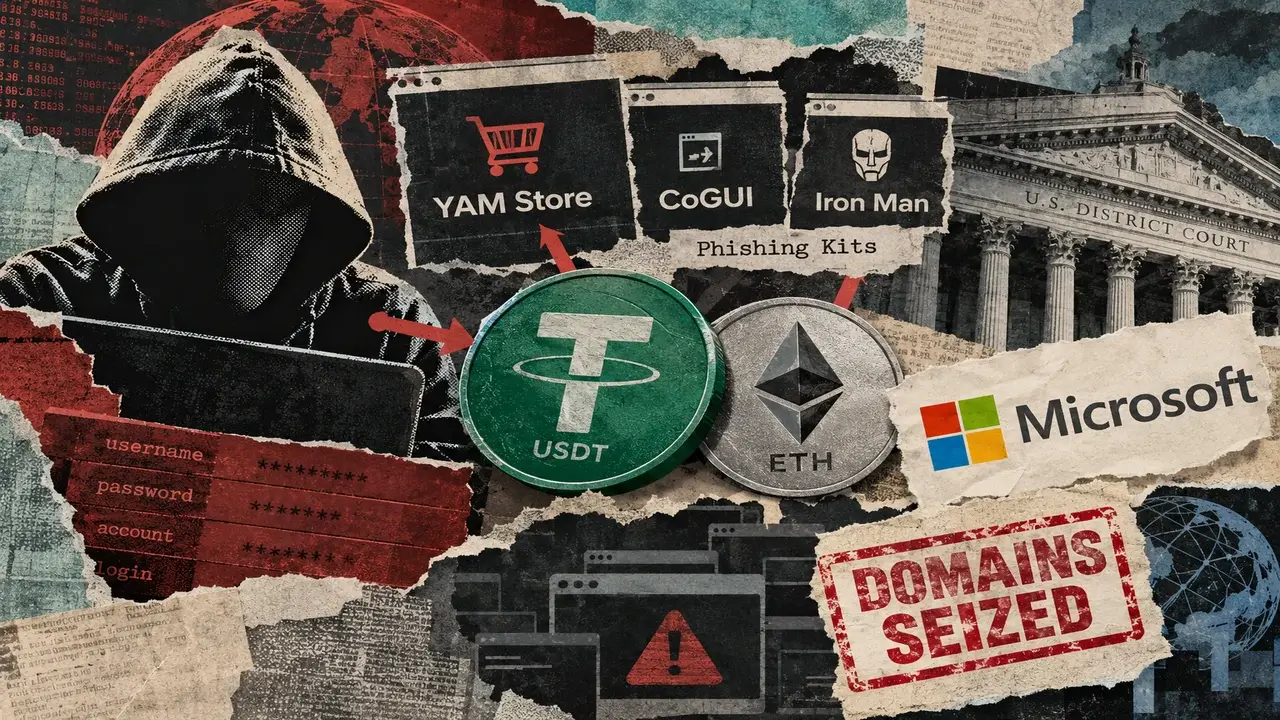
Microsoft and Health-ISAC obtained a US court order to seize and redirect domains used by YAM Store, CoGUI and Iron Man, services that sold compromised accounts and phishing tools. Microsoft says their operations supported campaigns targeting more than 75,000 organizations in over 150 countries and involved more than one billion phishing messages this year. The services accepted cryptocurrency, including USDT and USDC, alongside other payment methods. Microsoft disabled more than 20,000 linked accounts and is blocking associated domains; Cloudflare suspended related accounts and projects. TRM Labs helped investigators locate and freeze assets, but their value was not disclosed. Japan’s police and other industry and law-enforcement partners assisted, while related infrastructure remains under investigation.