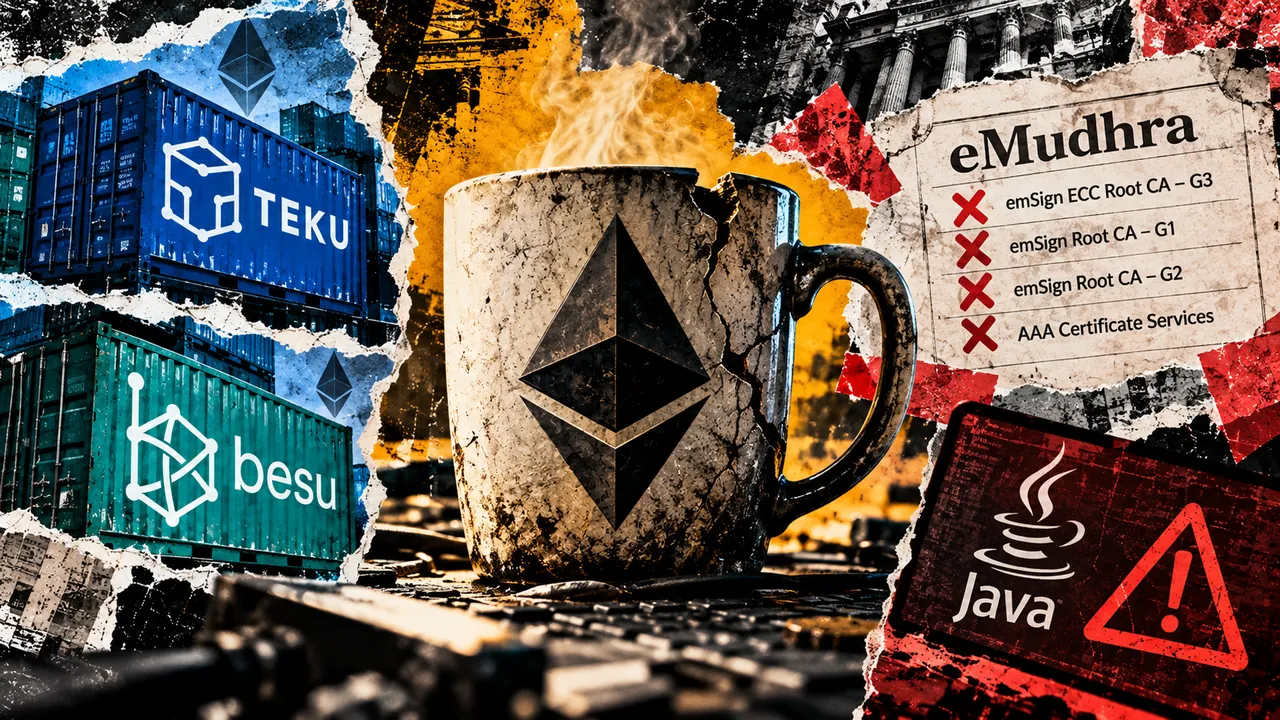
Ethereum client security fixes leave binary users with a separate Java check
Summary
Teku and Besu released Docker image updates that remove four certificate roots implicated in eMudhra’s compromised certificate-authority incident. The flaw affects HTTPS trust, but Teku says default mainnet nodes without HTTPS endpoints are not exposed, and no exploitation has been reported. Interception of an affected connection could allow endpoint impersonation, potentially disrupting validator duties or redirecting fees; impact depends on configuration. The fixes cover Docker images only. Operators using binary distributions must separately check and remediate their Java runtime, since revocation is not checked by default and updating the host Java does not update Java bundled in containers.