Rogue iPhone app escapes iOS sandbox to hijack $580,000 in USDT
Summary
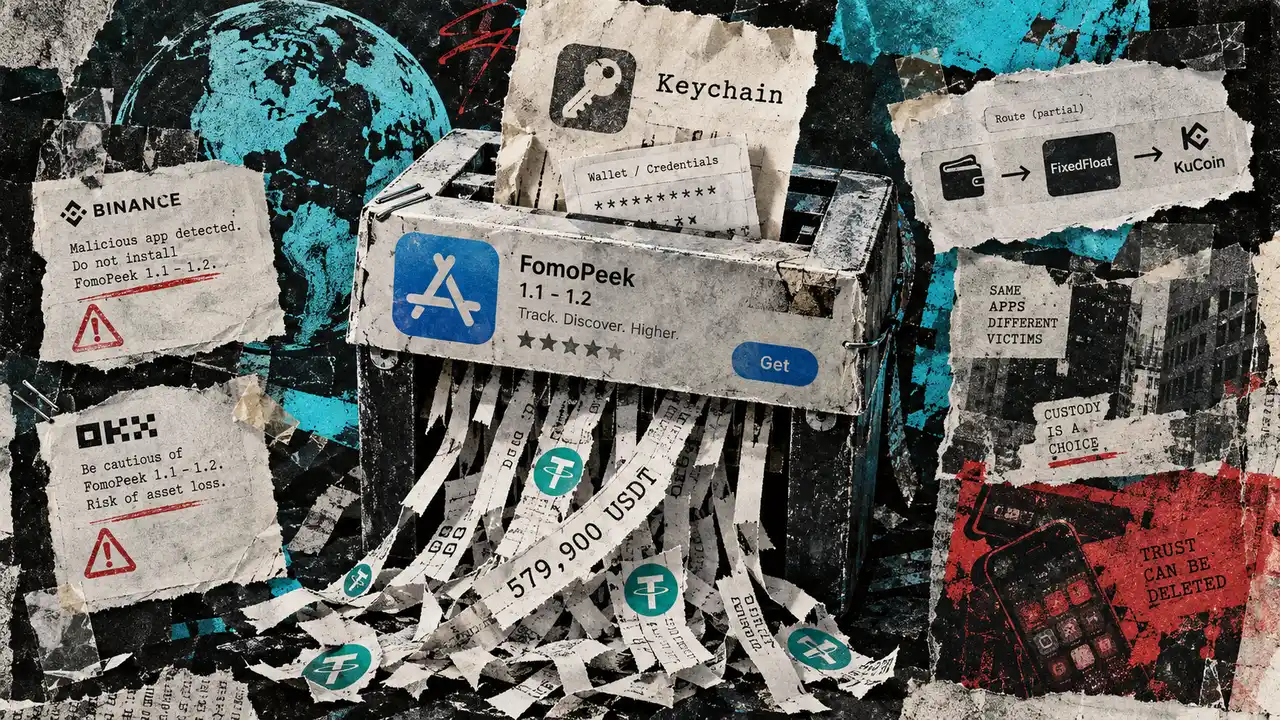
A malicious FomoPeek iPhone app distributed through Apple’s App Store stole an estimated 579,900 USDT, according to blockchain security firms SlowMist and Salus. Versions 1.1 and 1.2 contained command-and-control software and an exploit framework that could escape iOS’s app sandbox and access sensitive data, including locally stored wallet keys and credentials. The malicious modules were removed in version 1.3. Stolen funds were traced through several services and exchanges, while crypto platforms warned users to delete the app, update iOS, and move assets to newly created wallets on devices that never had FomoPeek installed. Deleting the app or updating the operating system may not protect keys that attackers already copied.