Who opened your crypto wallet before it reached your hands?
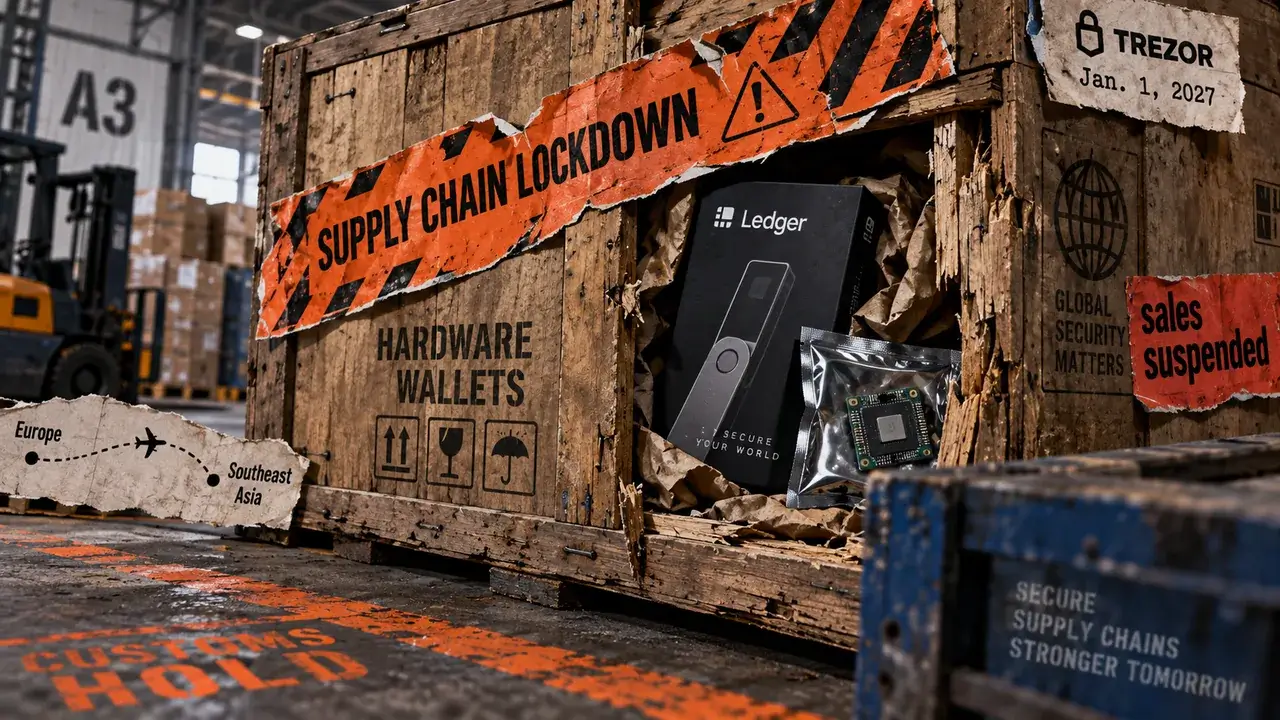
Ledger confirmed that a hardware implant in at least one genuine wallet sold through Southeast Asian authorized reseller CryptoBilis intercepted the 24-word recovery phrase during setup and sent it over LTE. The implant left the Secure Element and transaction-signing functions unchanged, so devices appeared authentic and operated normally. Bitquery estimates losses of $102 million across 324 wallets on six networks, a figure Ledger has not confirmed or linked wholly to implanted devices. Ledger said attackers modified genuine devices and returned them to distribution, then asked regional sellers to suspend sales and strengthened handling controls. It advised CryptoBilis customers to avoid initializing unused devices and to move funds from used devices to accounts created with a fresh recovery phrase. The incident highlights that hardware-wallet security depends on the whole device and supply chain, not only its protected chip.